


Offensive Security
Black-box and grey-box testing of web applications, from recon through to a written report a developer can act on.
- Web App Pentesting
- Bug Bounty
- XSS
- Injection
- Logic Flaws
- Access Control
- Responsible Disclosure
Riyadh, Kingdom of Saudi Arabia
I find and responsibly disclose real-world vulnerabilities in web applications, the CVEs I publish stand on the public record, and my reports are credited by the vendors who ship the fixes.
01, About
I'm Abdulaziz Alasaiqah, a 16-year-old penetration tester and bug bounty hunter based in Riyadh. My work centres on web application security, hunting for the logic flaws, injection points and access-control gaps that survive automated scanning, and reporting them through responsible disclosure.
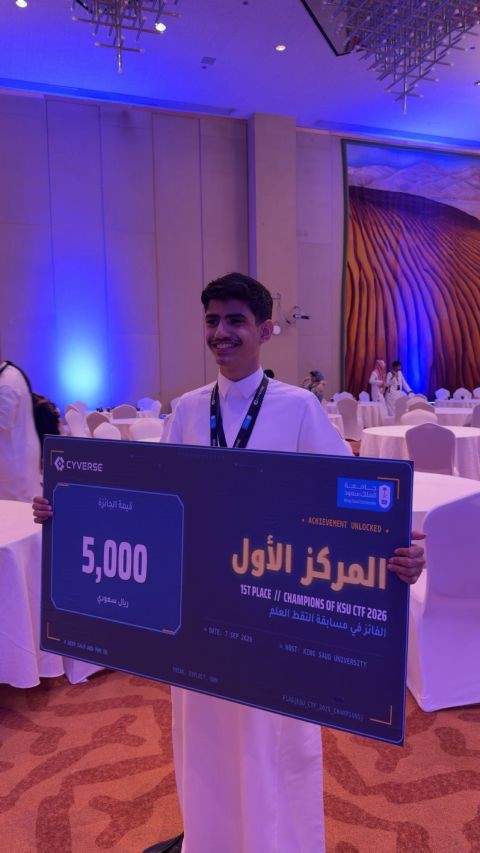
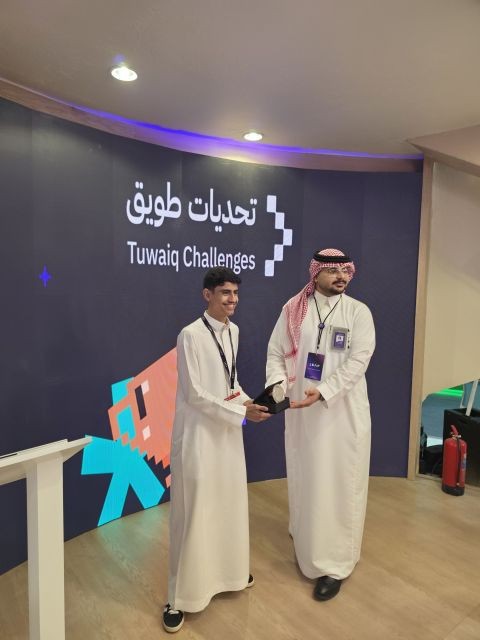
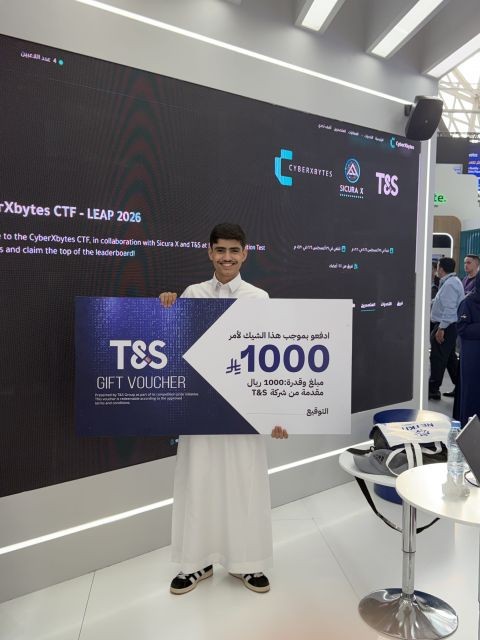
I'm an active researcher on BugBounty.sa, Saudi Arabia's national platform, where I've filed 132 reports for 1,500 points. Five of my findings are published CVEs, four of them in Firefox and patched by Mozilla, including one in Firefox 150 and ESR 140.10, and I've placed on the podium at seven security competitions and CTFs, including two 1st-place wins at KSU CTF 2026 and Tuwaiq Challenges, and Black Hat MEA 2025.
02, Track Record
Everything below is verifiable, published CVEs, platform credits and competition results.
Reported to Mozilla and patched in Firefox 150 and ESR 140.10. Awarded a 3,750 SAR bounty.
Discovered and responsibly disclosed; officially credited by the platform.
First place with 2 First Bloods, PixelVault (hard, web) and Dead Air (medium, pwn).
Champions with team Cybranos, 7,600+ team points. Personally claimed 10 of the team's 11 First Bloods and 18 of 25 flags.
Second place finish.
Third place, plus a First Blood in the reversing category as the first competitor to solve it.
Fourth place finish.
Third place at one of the region's largest cybersecurity gatherings.
Second place in the Defenseathon challenge.
Third place finish.
Active researcher, 132 reports filed across 1,500 points.
On the podium, click to enlarge.


03, Expertise
Black-box and grey-box testing of web applications, from recon through to a written report a developer can act on.
Chasing a finding all the way to a CVE, reproducing it, proving impact, and writing it up so the vendor can ship a fix.
Building the small tools the testing needs, scripting repetitive recon so the time goes into the interesting bugs.

04, The Kingdom
A proud citizen of the Kingdom of Saudi Arabia, working to strengthen its digital defenses.
Najd & Riyadh, click any frame to enlarge.


05, Contact
Open to penetration testing engagements, security research collaborations and full-time positions.
abdulazizalasaiqah@gmail.com